Cloud
We host and operate it, with an isolated database behind each account. HD voice, with geo routing in 100+ countries.
Put it in our cloud, in your building, or across both, and your team won't notice the difference. You decide what each person, bot, and API client can reach, and every change they make is written to one audit trail.
Your security team reviews one vendor instead of five.
100+ countries · Cloud, hybrid, or onsite · 1 to 1,000 seats
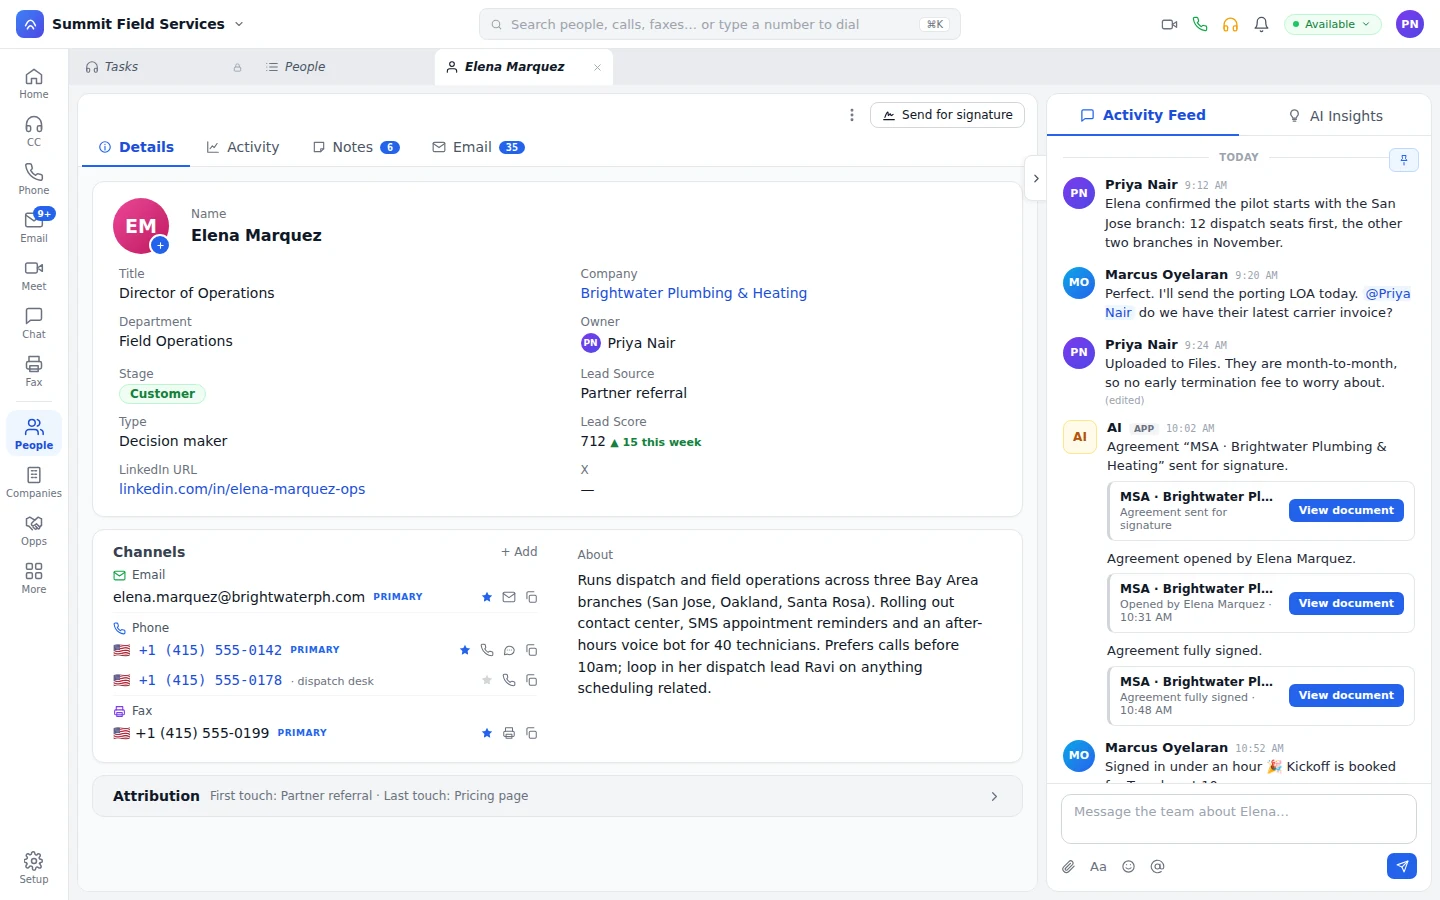
Phones, contact center, CRM, customer data, and marketing usually come from five vendors. Here's what that costs a reviewer, and what it looks like when it's one platform.
If your data can't live in someone else's cloud, you run the full platform on the Unbound appliance in your building. The mode only decides where it runs and who operates it. Your permissions and workflows come along to all three.
We host and operate it, with an isolated database behind each account. HD voice, with geo routing in 100+ countries.
Hybrid runs in your building and in our cloud together, active/active or active/passive, your choice. People sign in once, and admins run both from one console.
The whole platform on the Unbound appliance in your building, with the keys and backups in your hands. Calls, messages, records, files, and recordings stay in your building; we plan model calls and carrier traffic with you.
Your admins write policies point and click, or paste raw JSON. Every record carries a record type, and each person gets read, write, and update rights per type, so opening an object doesn't open every record in it. A bot is just another user with a policy, and its MCP calls show up in the audit trail next to everyone else's.
Click a policy together or type it out. Either way it runs through one engine.
People and integrations sign in over OAuth 2.0 and get a JWT that carries their policy, renewed for them.
Rights start at the object and narrow by record type, so a rep sees their types and nobody else's.
When someone changes a record or calls the API, you can see who it was and when, person or bot.
Outbound gets the same treatment. Set which countries a user, queue, or group can dial out to, and scope a blocklist, for voice and SMS, by number or prefix, to a user, group, or queue instead of the whole account.
Your operations people build the IVR, customer journeys, pre-queue steps, and team alerts themselves, on one canvas. They can pull outside MCP tools into any workflow and publish their own for other platforms to call, and a step can transfer a live call by API or software, not just from a device. When you want code, it's plain JavaScript.
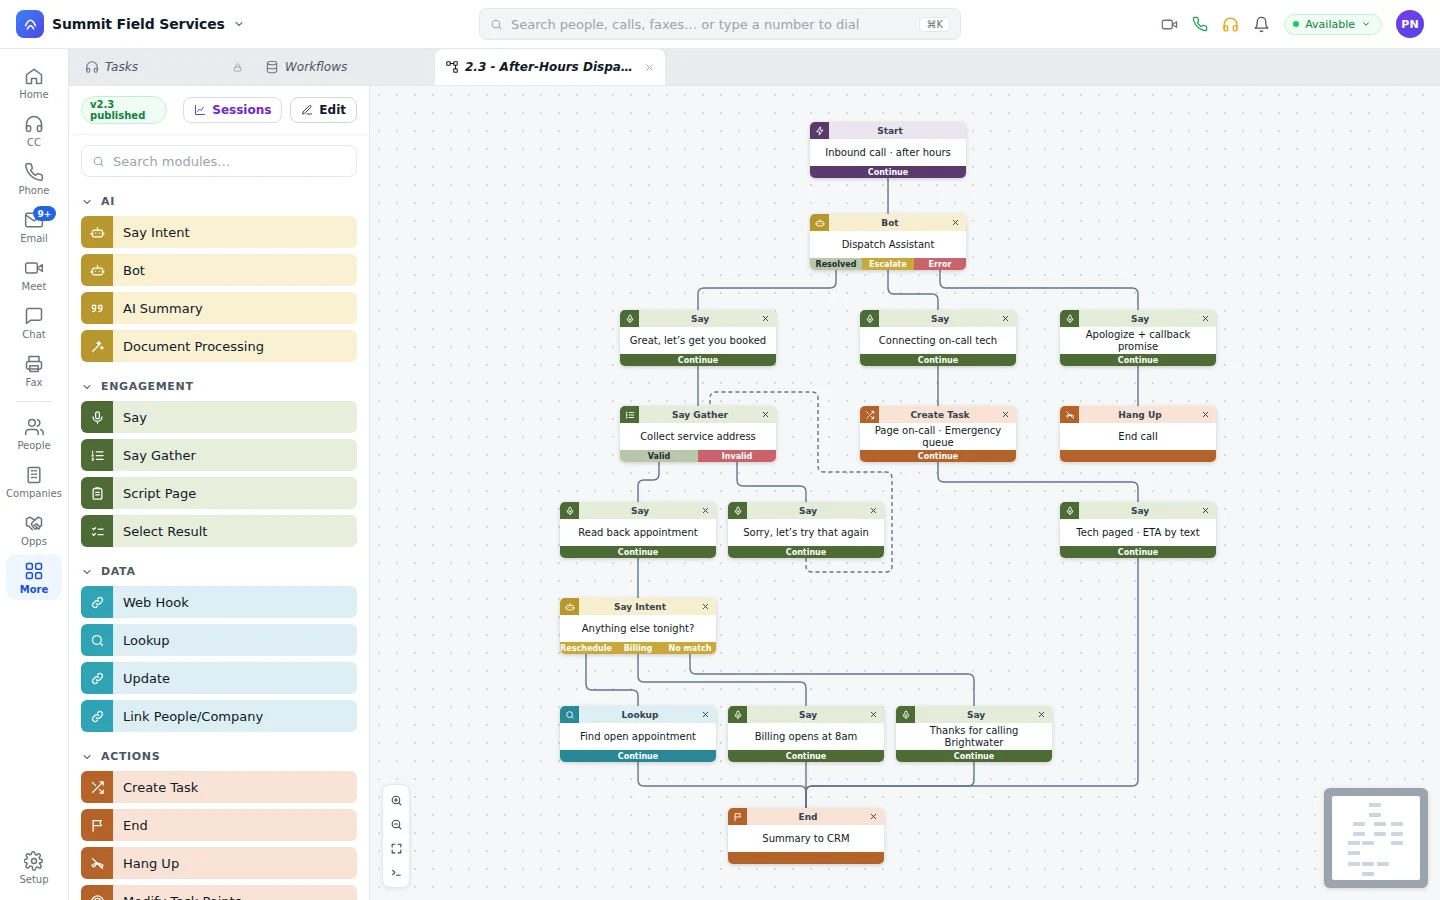
The caller hears the open times from your scheduling tool, picks one, and it's booked and on the record before anyone picks up.
A bot working a billing task takes the payment through the payment step and drops the receipt into the conversation.
A rep types an order number in a thread and gets the status back right there.
Native apps with every feature, plus a SIP desk phone for anyone who likes a handset. A five-person office starts on the same platform a large contact center runs, on SIP, media, and video engines we built ourselves.
Set the caller name your outbound calls show, per number, and on a desk phone, give each line key its own outbound caller ID.
Yes. Onsite isn't a fork: it gets every release cloud gets. The onsite card above lists what stays in your building and what we plan with you.
No. You grant read, write, and update per record type, so a person sees the record types their policy grants.
Only what you grant it, the way you'd grant it to the agent beside it. Scope a billing bot to billing record types and that's all it reads.
Yes. Every MCP call it makes lands in the audit trail your team's API calls land in.
Thinking hybrid or onsite? Send us your questionnaire and we'll plan it with you.